

Free SC-401 Exam Braindumps certification guide Q&A
SC-401 Certification Overview Latest SC-401 PDF Dumps
Microsoft SC-401 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 17
You have a Microsoft 365 E5 subscription.
You plan to implement insider risk management for users that manage sensitive data associated with a project.
You need to create a protection policy for the users. The solution must meet the following requirements:
# Minimize the impact on users who are NOT part of the project.
# Minimize administrative effort.
What should you do first?
- A. From the Microsoft Entra admin center, create a security group.
- B. From the Microsoft Purview portal create a priority user group
- C. From the Microsoft Entra admin center create a User risk policy
- D. From the Microsoft Purview portal, create an insider risk management policy.
Answer: B
Explanation:
Insider risk management policies in Microsoft Purview target users based on priority user groups.
If you want to monitor a specific project team, you must first define those users in a priority user group so that policies affect only them.
This approach:
Minimizes the impact on users not part of the project.
Reduces administrative effort since you don't need to manage multiple security groups in Entra ID.
Reference:
Microsoft Learn: Priority user groups in insider risk management
Quote: "To focus risk management policies on specific users...create and manage priority user groups in the Microsoft Purview compliance portal."
NEW QUESTION # 18
You have a Microsoft 365 E5 subscription.
You need to enable support for sensitivity labels in Microsoft SharePoint Online.
What should you use?
- A. the Microsoft Purview portal
- B. the SharePoint admin center
- C. the Microsoft 365 admin center
- D. the Microsoft Entra admin center
Answer: B
Explanation:
To enable support for sensitivity labels in Microsoft SharePoint Online, you must configure the setting in the SharePoint admin center.
Sensitivity labels in SharePoint Online allow labeling and protection of files stored in SharePoint and OneDrive. This feature must be enabled in the SharePoint admin center # Settings # Information protection to allow sensitivity labels to apply encryption and protection to stored documents.
NEW QUESTION # 19
You are creating a DLP policy named Policy1 that will be applied to the locations as shown in the following exhibit.
Policy1 contains an advanced data loss prevention (DLP) rule named Rule1.
Which two conditions can you use in Rule1? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. Content contains
- B. Document size equals or is greater than
- C. Document property is
- D. Content is shared from Microsoft 365
- E. Attachment's file extension is
Answer: A,D
Explanation:
You are creating a Data Loss Prevention (DLP) policy in Microsoft 365 with advanced rules. Advanced DLP rules provide more granular conditions and actions than standard DLP rules.
Conditions available in advanced DLP
According to Microsoft Docs on Conditions in DLP policies:
* # Content contains # Used to detect sensitive information types, keywords, or exact data matches.
This is one of the most common and fundamental DLP conditions.
* # Content is shared from Microsoft 365 # Used to detect whether content has been shared externally or with specific domains/users. This is a modern advanced DLP condition.
Why the others are not correct:
* A. Document property is # This condition applies to information governance retention policies /labels (not DLP). Not available in DLP rules.
* B. Attachment's file extension is # This is supported in Exchange mail flow rules (transport rules) but not in advanced DLP rules.
* C. Document size equals or is greater than # Also applies in Exchange transport rules and certain SharePoint restrictions, but not available as a DLP rule condition.
NEW QUESTION # 20
You have a Microsoft 365 E5 subscription. The subscription contains 500 Windows devices that are onboarded to Microsoft Purview.
You need to prevent users from sharing sensitive information with third-party generative AI websites.
Which Microsoft Purview solution should you use?
- A. Data Loss Prevention
- B. Information Protection
- C. Insider Risk Management
- D. Information Barriers
Answer: A
Explanation:
Considerations for DSPM for AI to manage data security and compliance protections for AI interactions To prevent users from sharing sensitive information with third-party generative AI websites when Windows devices are onboarded to Microsoft Purview, you can configure Data Loss Prevention (DLP) policies. These policies allow you to restrict access to specific service domains and block file uploads or sensitive data sharing with those domains.
Reference:
https://learn.microsoft.com/en-us/purview/dspm-for-ai-considerations
NEW QUESTION # 21
You recently discovered that the developers at your company emailed Azure Storage Account keys in plain text to third parties You need to ensure that when Azure Storage Account keys are emailed, the emails are encrypted.
Solution: You create a data loss prevention (DLP) policy that has Exchange email, SharePoint sites, OneDrive accounts, and Teams chat and channel messages selected.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
NEW QUESTION # 22
HOTSPOT
You plan to create a custom sensitive information type that will use Exact Data Match (EDM).
You need to identify what to upload to Microsoft 365, and which tool to use for the upload.
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: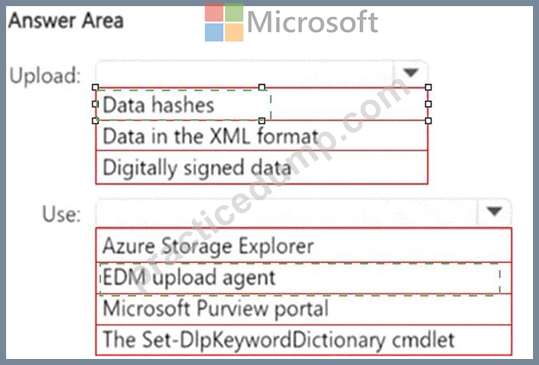
Explanation:
EDM does not store raw data; instead, it requires hashed versions of sensitive data for privacy and security.
To upload the hashed data, Microsoft provides the EDM upload agent. This ensures that the data is securely processed and recognized by the EDM service in Microsoft 365.
NEW QUESTION # 23
You have a Microsoft 565 subscription that contains 100 users and a Microsoft 365 group named Group1. All users have Windows 11 devices and use Microsoft SharePoint Online and Exchange Online. A sensitivity label named Label! is published as the default label for Group1. You add two sublabels named Sublabel1 and Sublabel2 lo Label1. You need to ensure that the settings in Sublabel 1 are applied by default to Group 1.
What should you do?
- A. Change the order of Sublabel!
- B. Duplicate all the settings from Sublabel! to Label1.
- C. Delete the policy of Label1 and publish Sublabel1.
- D. Modify the policy of Label1.
Answer: D
NEW QUESTION # 24
You have a Microsoft 365 E5 subscription that contains the groups shown in the following table.
The subscription contains the resources shown in the following table.
You create a sensitivity label named Label1.
You need to publish Label1 and have the label apply automatically.
To what can you publish Label1, and to what can Label1 be auto-applied? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Publishing a Sensitivity Label
Sensitivity labels can be published to Microsoft 365 groups, security groups, SharePoint Online sites, and Microsoft Teams. Since we have:
# Group1 (Microsoft 365 group) - Supported
# Group2 (Security group) - Supported
# Site1 (SharePoint Online site) - Supported
# Team1 (Microsoft Teams team) - Supported
This means we can publish Label1 to Group1, Group2, Site1, and Team1.
Box 2: Auto-Applying a Sensitivity Label
Auto-apply policies for sensitivity labels work on:
# SharePoint Online sites (documents)
# OneDrive (documents)
# Exchange email (messages)
However, labels cannot be auto-applied to Microsoft 365 groups or Teams directly because labels are applied to files and emails, not to groups or Teams as entities. Since Site1 (a SharePoint Online site) supports auto- apply, it is the correct option.
NEW QUESTION # 25
Hotspot Question
You have a Microsoft 365 subscription.
You plan to deploy an audit log retention policy.
You need to perform a search to validate whether the policy will be applied to the intended entries.
Which two fields should you configure for the search? To answer, select the appropriate fields in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
To validate whether an audit log retention policy will apply to the intended entries, you should configure the following fields:
- Date and time range (UTC) ensures that you are searching for audit logs within the time period when the policy should be applied. Audit logs are time-sensitive, and policies affect logs based on their timestamp.
- Record types allows you to filter and search for specific audit log categories (e.g., Exchange, SharePoint, Teams, etc.) that are affected by the retention policy. Selecting the correct record type ensures that the policy is evaluated against the relevant data.
NEW QUESTION # 26
You need to meet the technical requirements for the Site1 documents.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation:
A screenshot of a questionnaire AI-generated content may be incorrect.
The goal is to automatically label documents in Site1 that contain credit card numbers. To achieve this, we need a sensitivity label with an auto-labeling policy based on a sensitive info type that detects credit card numbers.
Step 1: Create a Sensitive Info Type
# A sensitive info type is needed to detect credit card numbers in documents.
# Microsoft Purview includes built-in sensitive info types for credit card numbers, but we can also create a custom one if necessary.
Step 2: Create a Sensitivity Label
# A sensitivity label is required to classify and protect documents containing sensitive information.
# This label can apply encryption, watermarking, or access controls to credit card data.
Step 3: Create an Auto-Labeling Policy
# An auto-labeling policy ensures that the sensitivity label is applied automatically when credit card numbers are detected in Site1.
# This policy is configured to scan files and automatically apply the correct sensitivity label.
NEW QUESTION # 27
Hotspot Question
You have a Microsoft 365 E5 subscription.
You plan to use the Microsoft Purview portal to map human resources (HR) data for use with insider risk management policies.
You need to add a data connector to import the HR data.
What should you do first, and in which format should you import the data? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Step 1: Prepare a CSV file with your HR data
Step 2: Create an app in Microsoft Entra ID
Step 3: Create the HR connector
Step 4: Run the sample script to upload your HR data
Step 5: Monitor the HR connector
(Optional) Step 6: Schedule the script to run automatically
(Optional) Step 7: Upload data by using Power Automate templates
Reference:
https://learn.microsoft.com/en-us/purview/import-hr-data
NEW QUESTION # 28
You have a Microsoft 365 E5 subscription that uses Microsoft Purview.
You need ensure that an incident will be generated when a user visits a phishing website.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 29
You have a Microsoft J65 E5 subscription that contains a user named User1.
All users are assigned Microsoft 365 Copilot licenses.
You deploy Microsoft Purview Data Security Posture Management for Al (DSPM for Al).
You need to ensure that User1 can analyze prompts and responses for Al interaction events. The solution must follow the principle of least privilege.
To which two role groups should you add User1? Each correct answer presents part of the solution.
NOTE; Each correct selection is worth one point.
- A. Insider Risk Management Investigators
- B. Content Explorer list Viewer
- C. Information Protection Analysts
- D. Security Reader
- E. Content Explorer Content Viewer
Answer: B,E
NEW QUESTION # 30
You receive an email that contains a list of words that will be used fora sensitive information type.
You need to create a file that can be used as the source of a keyword dictionary.
In which format should you save the list?
- A. a CSV file that contains words separated by commas
- B. an XLSX file that contains one word in each cell of the first row
- C. a TSV file that contains words separated by tabs
- D. an ACCDB database file that contains a table named Dictionary
Answer: A
Explanation:
Correct:
* a CSV file that contains words separated by commas
* a text file that has one word on each line
Incorrect:
* an ACCDB database file that contains a table named Dictionary
* a DOCX file that has one word on each line
* a JSON file that has an element for each word
* a TSV file that contains words separated by tabs
* an XML file that contains a keyword tag for each word
* an XLSX file that contains one word in each cell of the first row
Note:
To create a keyword dictionary for a sensitive information type in Microsoft Purview Data Loss Prevention (DLP), you must use a plain text (.txt) file (or a .CSV file) where each keyword is on a separate line.
Format Example (TXT file):
confidential
sensitive
classified
top secret
This format is simple, efficient, and directly compatible with Microsoft 365 DLP policies for keyword dictionaries.
How to use the keyword dictionary?
Create a text file with one keyword per line.
Upload it to Microsoft Purview under Data Classification > Sensitive Info Types.
Use the dictionary in a DLP policy to identify and protect sensitive information.
In steps:
Create a keyword dictionary using the Microsoft Purview portal
Use these steps to create or import keywords for a custom dictionary:
1. Sign in to the Microsoft Purview portal Information Protection > Classifiers > Sensitive info types.
2. Select + Create sensitive info type and then enter a Name and Description for your sensitive info type. Choose Next.
3. On the Define patterns for this sensitive info type page, choose + Create pattern.
4. In the New pattern window, select a Confidence level.
5. Choose Add a Primary element and select Keyword dictionary.
*-> 6. On the Add a keyword dictionary flyout, you can:
6a.Upload a dictionary file in TXT or CSV format.
6b. Choose from existing dictionaries.
or create a new dictionary by entering keywords manually and giving it a name.
Reference:
https://learn.microsoft.com/en-us/purview/sit-create-a-keyword-dictionary
NEW QUESTION # 31
You have a Microsoft 365 E5 tenant.
You create a data loss prevention (DLP) policy.
You need to ensure that the policy protects documents in Microsoft Teams chat sessions.
Which location should you enable in the policy?
- A. Teams chat and channel messages
- B. Exchange email
- C. OneDrive accounts
- D. SharePoint sites
Answer: C
Explanation:
Documents shared in Team Chats are stored in OneDrive and shared in Channel Chats are stored in SharePoint Sites.
NEW QUESTION # 32
You have a data loss prevention (DIP) policy that has the advanced DIP rules shown in the following table.
You need to identity which rules will apply when content matches multiple advanced DIP rules.
Which rules should you identify? To answer, select the appropriate options in the answer area.
Answer:
Explanation: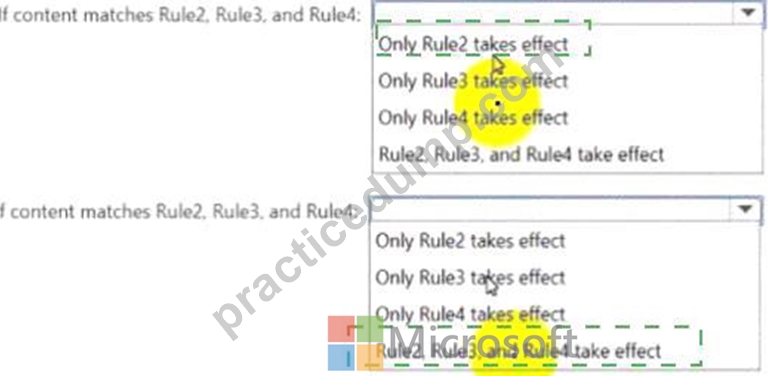
Explanation:
NEW QUESTION # 33
Case Study 1 - Contoso, Ltd
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and three branch offices in Seattle, Boston, and Johannesburg.
Existing Environment
Microsoft 365 Environment
Contoso has a Microsoft 365 E5 tenant. The tenant contains the administrative user accounts shown in the following table.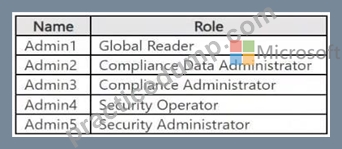
Users store data in the following locations:
- SharePoint sites
- OneDrive accounts
- Exchange email
- Exchange public folders
- Teams chats
- Teams channel messages
When users in the research department create documents, they must add a 10-digit project code to each document. Project codes that start with the digits 999 are confidential.
SharePoint Online Environment
Contoso has four Microsoft SharePoint Online sites named Site1, Site2, Site3, and Site4.
Site2 contains the files shown in the following table.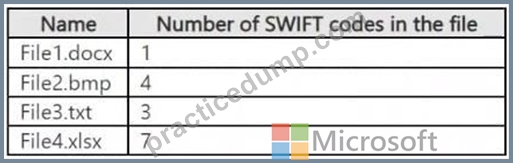
Two users named User1 and User2 are assigned roles for Site2 as shown in the following table.
Site3 stores documents related to the company's projects. The documents are organized in a folder hierarchy based on the project.
Site4 has the following two retention policies applied:
- Name: Site4RetentionPolicy1
Locations to apply the policy: Site4
Delete items older than: 2 years
Delete content based on: When items were created
- Name: Site4RetentionPolicy2
Locations to apply the policy: Site4
Retain items for a specific period: 4 years
Start the retention period based on: When items were created
At the end of the retention period: Do nothing
Problem Statements
Management at Contoso is concerned about data leaks. On several occasions, confidential research department documents were leaked.
Requirements
Planned Changes
Contoso plans to create the following data loss prevention (DLP) policy:
- Name: DLPpolicy1
Locations to apply the policy: Site2
Conditions:
Content contains any of these sensitive info types: SWIFT Code
- Instance count: 2 to any
Actions: Restrict access to the content
Technical Requirements
Contoso must meet the following technical requirements:
- All administrative users must be able to review DLP reports.
- Whenever possible, the principle of least privilege must be used.
- For all users, all Microsoft 365 data must be retained for at least
one year.
- Confidential documents must be detected and protected by using
Microsoft 365.
- Site1 documents that include credit card numbers must be labeled
automatically.
- All administrative users must be able to create Microsoft 365
sensitivity labels.
- After a project is complete, the documents in Site3 that relate to
the project must be retained for 10 years.
Hotspot Question
You are reviewing policies for the SharePoint Online environment.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.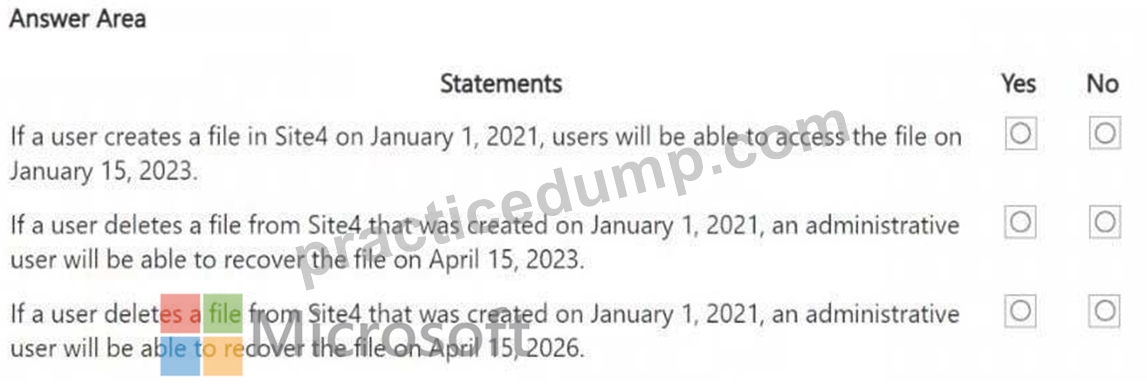
Answer:
Explanation:
Explanation:
Understanding Site4's Retention Policies:
- Site4RetentionPolicy1 deletes items older than 2 years from creation. If a file was created on January 1, 2021, it would be deleted after January 1, 2023.
- Site4RetentionPolicy2 retains files for 4 years from creation. If a file was created on January 1,
2021, it will be kept until January 1, 2025, but not deleted after that (policy states "Do nothing").
Box 1 - Yes, because Site4RetentionPolicy2 ensures files are retained for 4 years.
Box 2 - Yes, because Site4RetentionPolicy2 retains the file for 4 years (until January 1, 2025).
Box 3 - No, because retention is only for 4 years (until January 1, 2025). After that, the policy does "nothing," meaning the file is no longer recoverable after that period.
NEW QUESTION # 34
You have a Microsoft 36S subscription.
In Microsoft Exchange Online, you configure the mail flow rule shown in the following exhibit.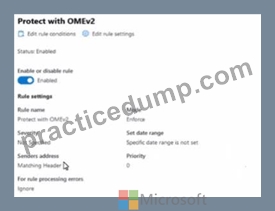
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation: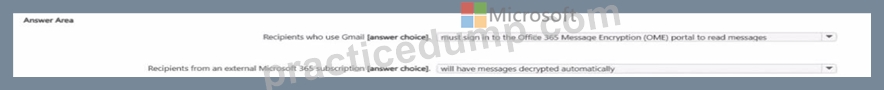
The mail flow rule is configured to apply OMEv2 protection ("Protect with OMEv2") to messages. With OMEv2:
Recipients on consumer mail systems (such as Gmail) receive a link-protected message and must authenticate to the Office 365 Message Encryption portal to view the content.
Microsoft 365 recipients (even in external tenants) get a native reading experience in Outlook/OWA where protected messages are opened directly with automatic decryption using their Microsoft 365 identity-no separate OME portal workflow is required.
These behaviors are documented by Microsoft for OMEv2 user experiences for different recipient types and clients. See: Microsoft Purview Office 365 Message Encryption overview and user experiences for external Microsoft 365 and consumer email recipients.
NEW QUESTION # 35
You have a Microsoft 365 E5 subscription that uses Microsoft Purview.
You are evaluating the use of custom data assessment scans to identify the potential oversharing of data in the subscription.
What is the maximum number of items the data assessments can support per location?
- A. 100.000
- B. 500.000
- C. 50.000
- D. 200.000
Answer: D
NEW QUESTION # 36
SIMULATION
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and select the username below.
To enter your password, place your cursor in the Enter password box and select the password below.
Microsoft 365 Username:
[email protected]
Microsoft 365 Password: XXXXXXXXX
If the Microsoft Edge browser or Microsoft 365 portal does not load successfully, select the Microsoft Edge browser icon from the task bar, type the URL "https://admin microsoft.com", and press Enter.
The following information is for technical support purposes only:
Lab Instance: XXXXXXXX.
Task 3
You plan to automatically apply a watermark to the documents of a project named Falcon.
You need to create a label that will add a watermark of "Project Falcon" in red, size-12 font diagonally across the documents.
Answer:
Explanation:
Create and configure sensitivity labels
Step 1: From the Microsoft Purview compliance portal, select Solutions > Information protection > Labels Step 2: On the Labels page, select + Create a label to start the new sensitivity label configuration:
Step 3: On the Define the scope for this label page, the options selected determine the label's scope for the settings that you can configure and where they'll be visible when they're published.
In our case select: Items, Files, and select Word documents.
Note: If Items is selected, you can configure settings that apply to apps that support sensitivity labels, such as Office Word and Outlook. Optionally, you can extend these labels to include meetings from Teams and Outlook, and to protecting Teams meetings themselves by enforcing settings for Teams meetings and related chat.
Step 4: Follow the configuration prompts for the label settings. Use the help in the UI for individual settings.
Step 5: In the UI add a watermark of "Project Falcon" in red, size-12 font diagonally across the document.
Note: What sensitivity labels can do
After a sensitivity label is applied to an email, meeting invite, or document, any configured protection settings for that label are enforced on the content. You can configure a sensitivity label to:
* Mark the content when you use Office apps, by adding watermarks, headers, or footers to email, meeting invites, or documents that have the label applied. Watermarks can be applied to documents but not email or meeting invites. Example header and watermark: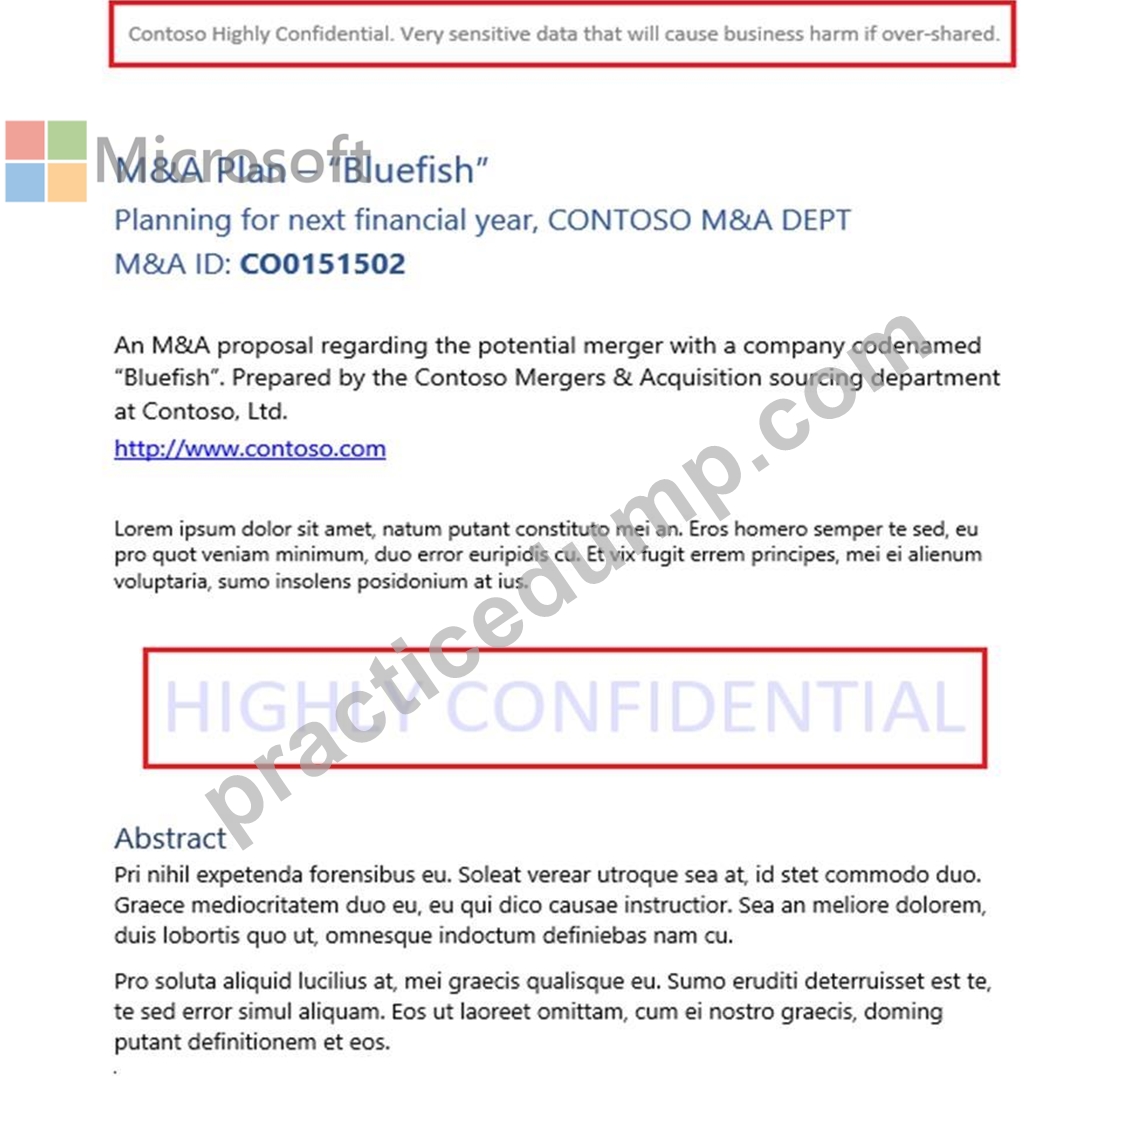
Step 6: Finish the Wizard
Reference:
https://learn.microsoft.com/en-us/purview/create-sensitivity-labels
https://answers.microsoft.com/en-us/msteams/forum/all/how-to-automatically-apply-sensitivity- labels-to/2482d1b2-1fe6-4a80-af4a-2b93b9c670de
NEW QUESTION # 37
You have a Microsoft 365 E5 subscription that contains a trainable classifier named Trainable1.
You plan to create the items shown in the following table.
Which items can use Trainable 1?
- A. Label1 and Policy1 only
- B. Label2 only
- C. Label2, Policy1, and DLP1 only
- D. Label1 and Label2 only
- E. Label1, Label2, Policy1, and DLP1
Answer: C
Explanation:
A trainable classifier in Microsoft Purview is used to automatically identify and classify unstructured data based on content patterns. The classifier can be used in:
1. Retention Labels (Label2) Supported
Trainable classifiers can be linked to retention labels to automatically classify and apply retention policies to documents.
2. Retention Label Policies (Policy1) Supported
Retention label policies define how and where retention labels are applied, including automatically using trainable classifiers.
3. Data Loss Prevention (DLP) Policies (DLP1) Supported
Trainable classifiers can be used in DLP policies to detect and protect sensitive content automatically.
NEW QUESTION # 38
You have Microsoft 365 E5 subscription that uses data loss prevention (DLP) to protect sensitive information.
You have a document named Form.docx.
You plan to use PowerShell to create a document fingerprint based on Form.docx.
You need to first connect to the subscription.
Which cmdlet should you run?
- A. Connect-SPOService
- B. Connect-ExchangeOnline
- C. Connect-MgGraph
- D. Connect-IPPSSession
Answer: D
Explanation:
Currently, you can create a document fingerprint only in Security & Compliance PowerShell, and Connect-IPPSSession is how you connect to it.
https://learn.microsoft.com/en-us/purview/document-fingerprinting#create-a-custom-sensitive- information-type-based-on-document-fingerprinting-using-powershell
https://learn.microsoft.com/en-us/powershell/module/exchange/connect-
ippssession?view=exchange-ps
NEW QUESTION # 39
......
The Best Microsoft SC-401 Study Guides and Dumps of 2026: https://torrentpdf.practicedump.com/SC-401-exam-questions.html